
Accountability
Complying is not enough: you must be able to demonstrate it with records, policies and evidence.
Regulation (EU) 2016/679 · GDPR
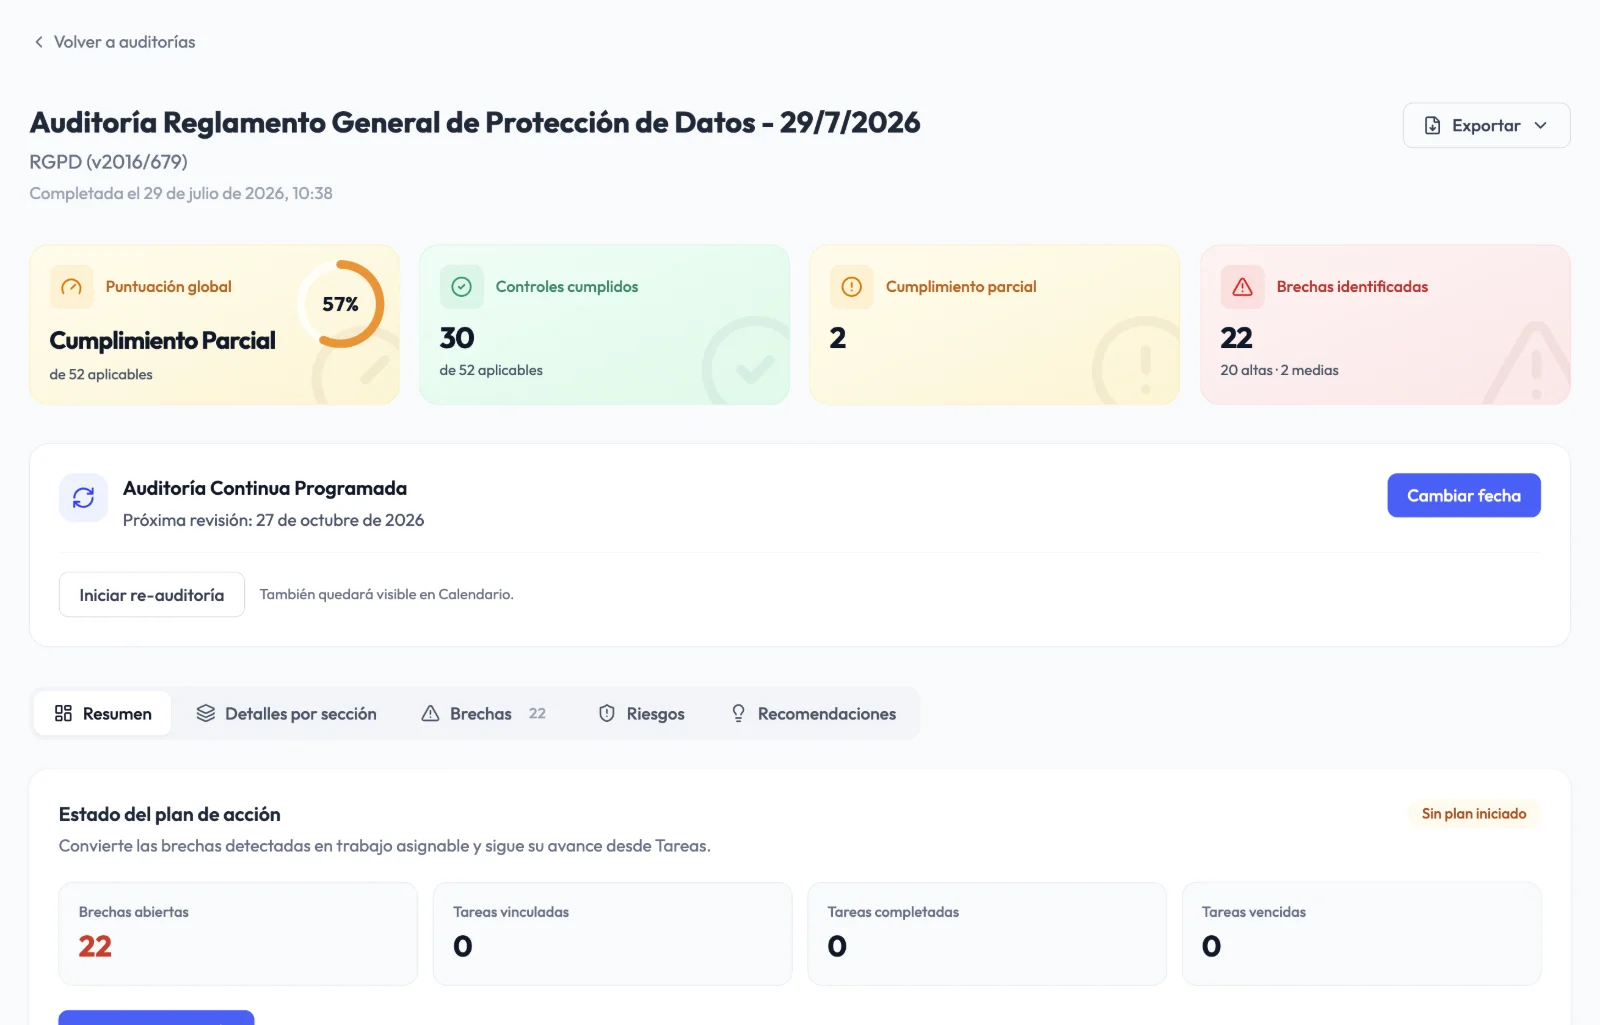
Audexa turns data protection into a measurable program: a 52-control audit, privacy policies and procedures, suppliers with data processing agreements and evidence ready if the data protection authority comes knocking.
Why now
Enforcement is real. In Spain alone, the data protection authority (AEPD) received 30,931 complaints in 2025, 64% more than the year before, and imposed more than €48 million in fines, with security breaches accounting for 40% of that amount.
Complying is not enough: you must be able to demonstrate it with records, policies and evidence.
Every supplier that processes data on your behalf needs a data processing agreement and oversight.
Notification to the supervisory authority within 72 hours when there is a risk, and a record of every breach.
Procedures to handle access, rectification, erasure, objection and portability requests on time.
DPIAs for high-risk processing and prior consultation where required.
Appropriate safeguards when data leaves the European Economic Area.
Sources: AEPD (Spain): 2025 annual report (in Spanish) · Regulation (EU) 2016/679 (EUR-Lex)
How Audexa helps
Assess, document and monitor in the same place where you manage information security.
Know where you stand against the regulation.
52 controls across 8 areas, with interpretation guidance and remediation steps.
43 mappings to build on your security evidence.
Compare progress between reviews with the same scope.
The policies you'll be asked for.
Privacy policy, data retention and protection of personal data in the cloud.
Data subject rights, data protection impact assessment (DPIA) and personal data breach management.
Versions, review, approval and signature with full traceability.
Suppliers and data under control.
Spot SaaS apps and suppliers that process personal data without a data processing agreement.
Record where the data of each application and supplier is hosted.
Contracts, records and certificates with review and expiry dates.
Some features depend on your plan and active modules.
How it works
Complete the GDPR audit and get your prioritized gaps.
Approve policies and procedures, sign data processing agreements and assign tasks.
Keep evidence current and share the report with management or your DPO.
Before and after
Compliance status
Opinion, not data
Score by area and progress over time
Suppliers
Lost data processing agreements
SaaS and suppliers with DPA status at a glance
Procedures
Generic downloaded templates
Versioned, approved procedures
Security
Separate from privacy
Connected with ISO 27001
Frequently asked questions
No. Audexa is the tool your DPO or privacy lead uses to measure, document and monitor compliance. Decisions and advice remain theirs.
The audit is based on the GDPR, the core regulation, and includes areas such as marketing, cookies and digital processing. National specifics, such as Spain's LOPDGDD, are handled in your policies and procedures.
Yes. The audit assesses your ability to detect and report breaches, and the library includes a personal data breach management procedure ready to adapt.
The GDPR framework is available on the Premium and Diamond plans.
Audexa runs on EU infrastructure, with role-based access, two-factor authentication and activity traceability.
Request a demo
In 30 minutes we walk through the GDPR audit, privacy policies and oversight of suppliers and data processing agreements.