
Context and scope
Define the ISMS scope, the interested parties and the requirements that apply to the organization.
ISO/IEC 27001:2022
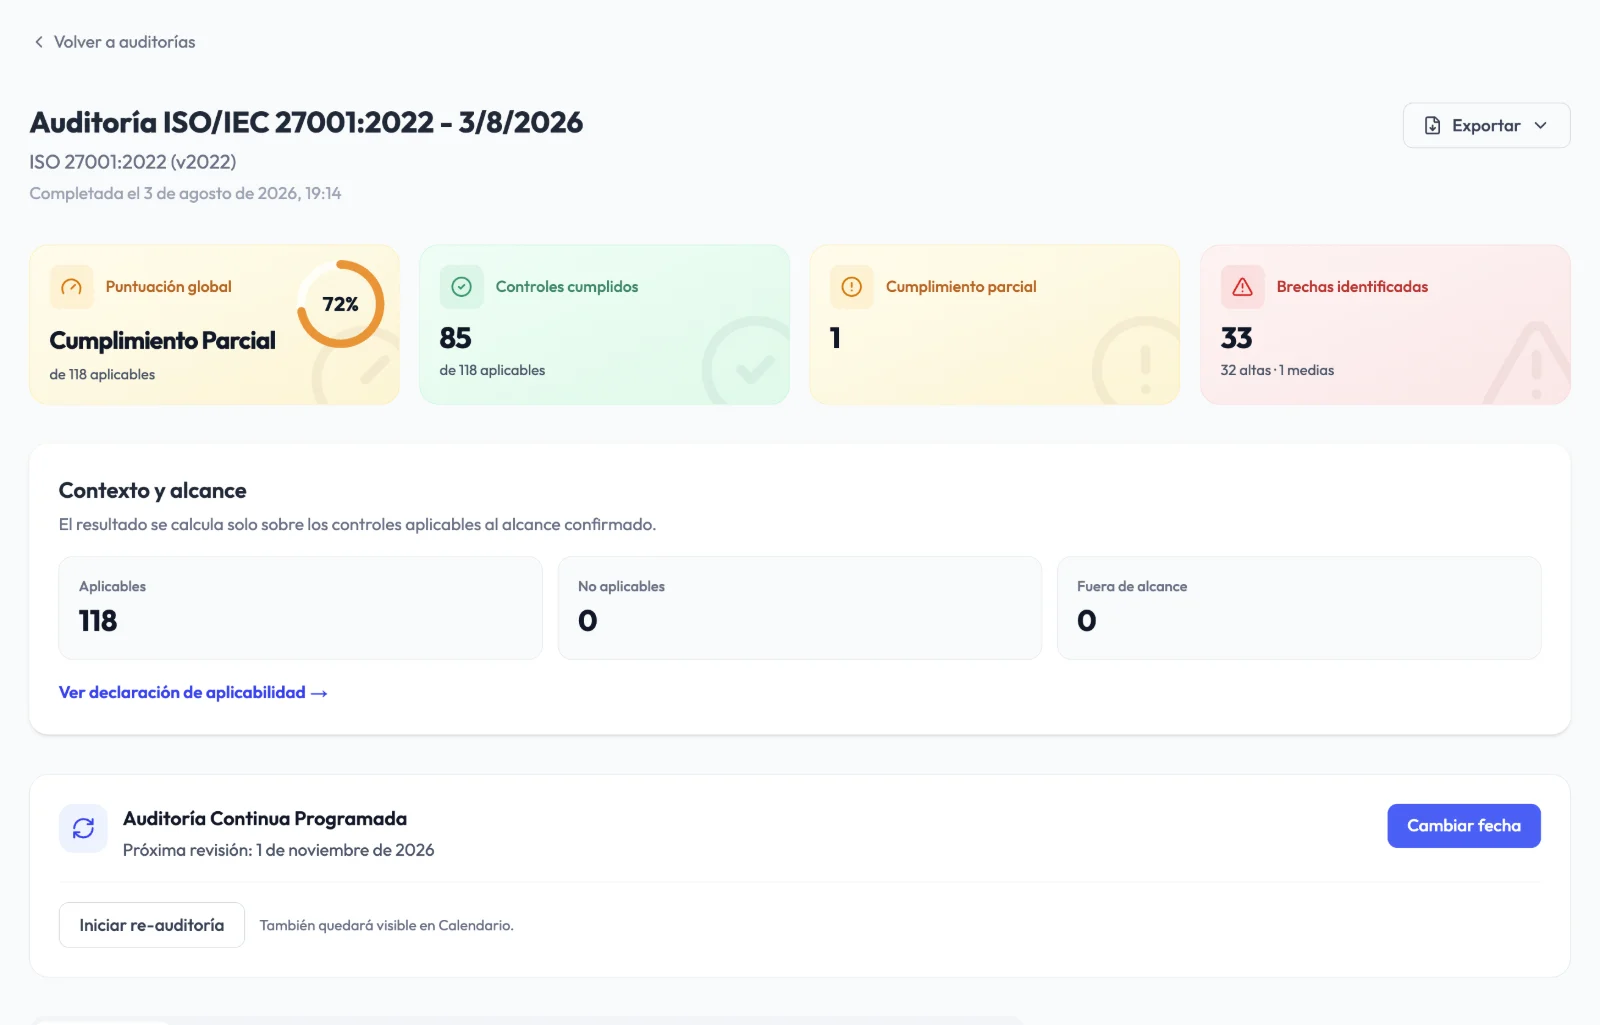
Audexa organizes your ISMS in a single workspace: clauses and Annex A assessed control by control, a Statement of Applicability, approved policies, evidence with expiry dates and an action plan to get you to the certification audit.
What the standard requires
The 2022 edition reorganized Annex A into 93 controls and four themes. The transition from the 2013 edition ended on October 31, 2025, so valid certificates must now be on the 2022 edition.
Define the ISMS scope, the interested parties and the requirements that apply to the organization.
Top management approves the information security policy, assigns roles and provides resources.
A repeatable risk method and a treatment plan consistent with the selected controls.
Which Annex A controls apply, which don't and why, with their implementation status.
Records, procedures and proof that controls work, not just that they exist.
Internal audit, management review and corrective actions to close the loop.
How Audexa helps
Assess, decide applicability, carry out remediation and keep the evidence without relying on shared folders.
Know the status of every clause and control.
Clauses 4 to 10 and Annex A grouped by theme, with guidance, weighting and remediation steps.
Repeat the audit with the same scope and compare progress between cycles.
Answers with high coverage are suggested as reviewable drafts in NIS2, ENS or GDPR.
Decisions and work with full traceability.
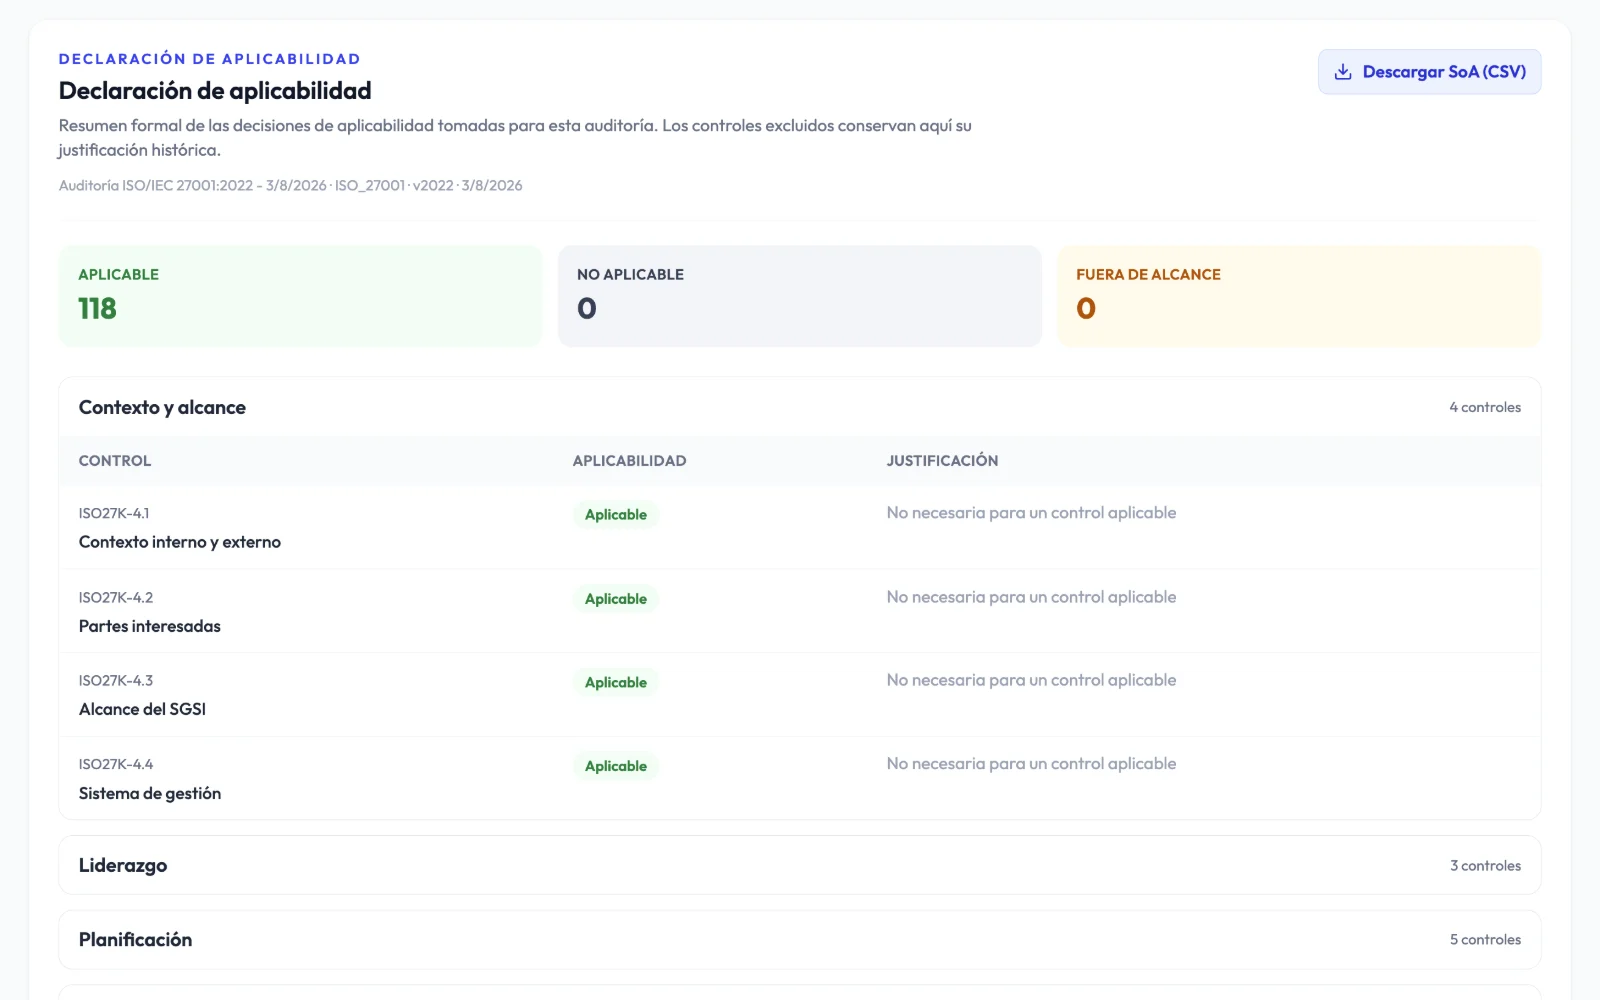
Mark controls as applicable, not applicable or out of scope with a justification, and export them.
Likelihood and impact matrix, treatment and risk acceptance signed by management.
Devices, software, SaaS and suppliers with an owner and periodic review.
Organized evidence for auditors.
43 templates linked to ISO 27001 with versions, approval and signature.
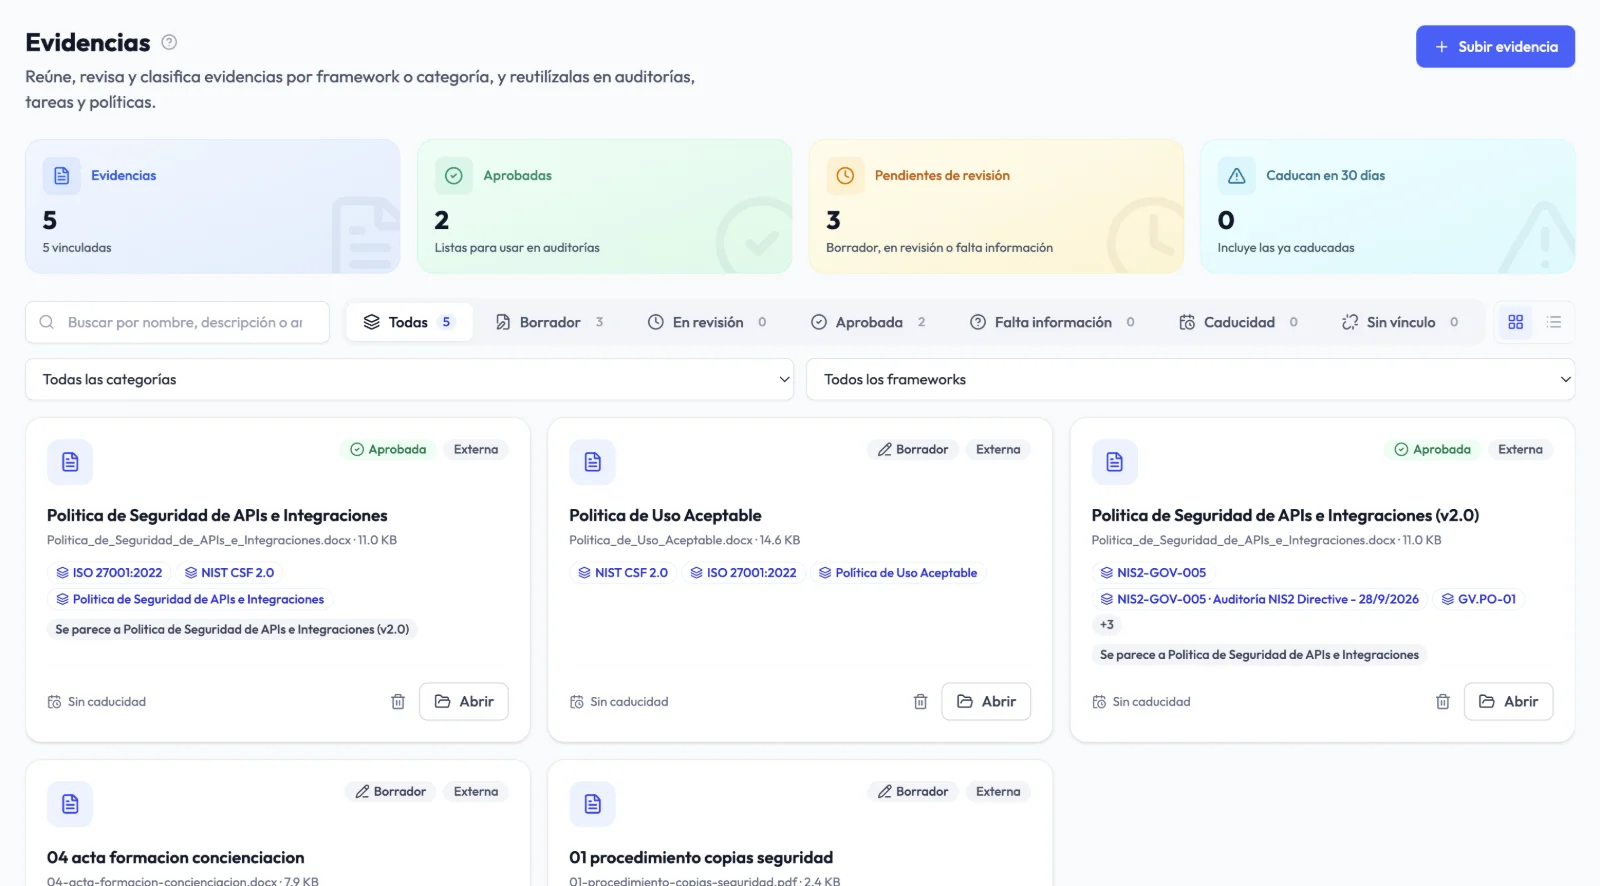
Documents with an owner, review, expiry and history, linked to each control.
A ZIP with an index, a summary and only approved evidence to share with the auditor.
Some features depend on your plan and active modules.
Statement of Applicability
Before answering, decide which controls apply. Every exclusion keeps its justification, and the statement is exported with the organization's context and the applicability of each control.
Evidence
Upload a document once and link it to controls, tasks, policies or risks. Audexa tracks its expiry and review so you never present out-of-date proof.
How it works
Assess the clauses and Annex A and get your score, your gaps and an executive report.
Turn gaps into tasks, approve policies and link evidence to each control.
Re-audit, compare progress and share the evidence pack with your auditor.
Before and after
Statement of Applicability
Excel disconnected from reality
Generated from the audit itself
Evidence
Folders with questionable versions
Vault with expiry, review and history
Policies
Word files without version control
Templates with approval and signature
Follow-up
Gaps in a static report
Tasks with owners and re-audits
Other frameworks
Starting from scratch for NIS2 or ENS
Reusable, reviewable answers
Frequently asked questions
Yes. The Free plan includes a complete ISO 27001 audit, an executive report in PDF and the tasks derived from the audit. You can sign up at app.audexa.es or ask us for a guided demo.
No. Certification is issued by an accredited certification body. Audexa helps you implement and maintain your ISMS and prepare the evidence and reports for the audit.
Yes. The audit follows the 2022 edition: clauses 4 to 10 and the 93 Annex A controls grouped into organizational, people, physical and technological controls.
Yes. You set the applicability of each control with its justification and export it together with the organization's context and the framework version.
Yes. Audexa includes mappings from ISO 27001 to NIS2, ENS, GDPR, NIST CSF 2.0, ISO 9001 and ISO 14001 so you can reuse evidence and reviewable answers.
Audexa runs on EU infrastructure, with role-based access, two-factor authentication and activity traceability.
Request a demo
In a 30-minute demo we walk through the audit, the Statement of Applicability, policies and the evidence pack.