
From finding to scenario
A gap says what's missing; a risk explains what could happen, who it affects and how much it matters.
Risk management
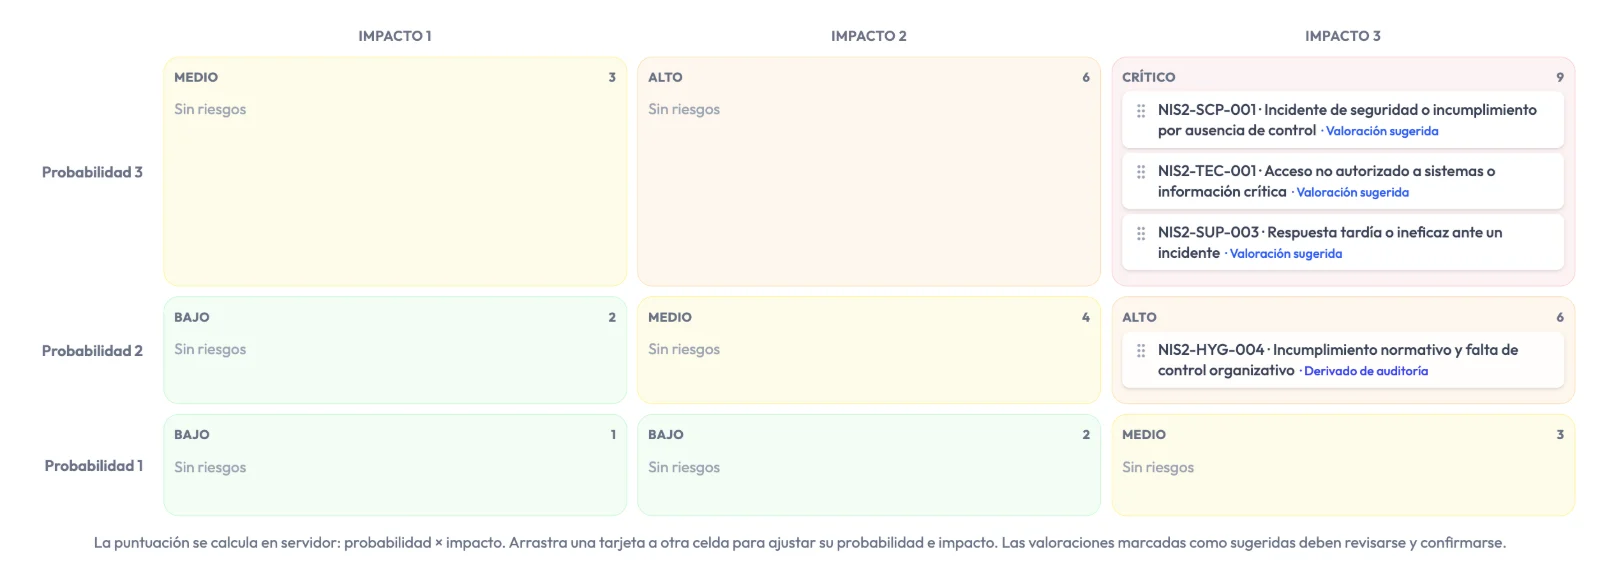
Every audit gap becomes a risk with a scenario, likelihood and impact. Audexa places them on a matrix, helps you decide whether to mitigate, accept or transfer them and keeps management's signed approval.
Why it matters
ISO 27001, NIS2, DORA, ENS and ISO 22301 all start from a risk analysis. Authorities and auditors want to see that risks are assessed, that someone decides what to do about them and that management approves it.
A gap says what's missing; a risk explains what could happen, who it affects and how much it matters.
Every treatment has an owner, a date and a verifiable closure criterion.
Accepting or transferring a risk is a governance decision that must be documented and signed.
How Audexa helps
Risks don't live in an isolated matrix: they come from audits and are closed with tasks and evidence.
Risks that come from the data.
Every Partial or No answer generates a risk with a suggested, reviewable scenario.
Likelihood and impact suggested based on gap severity, control weight and context.
vRadar adds a 0–100 risk score to CVE findings on your assets.
Decide and execute.
Drag each risk across the nine cells and recalculate its level: low, medium, high or critical.
With a justification, owner, date and residual risk rating.
Mitigation becomes tasks with recommended steps and expected evidence.
Documented risk governance.
A signature tied to the exact version of the risk; if anything relevant changes, the signature is no longer valid.
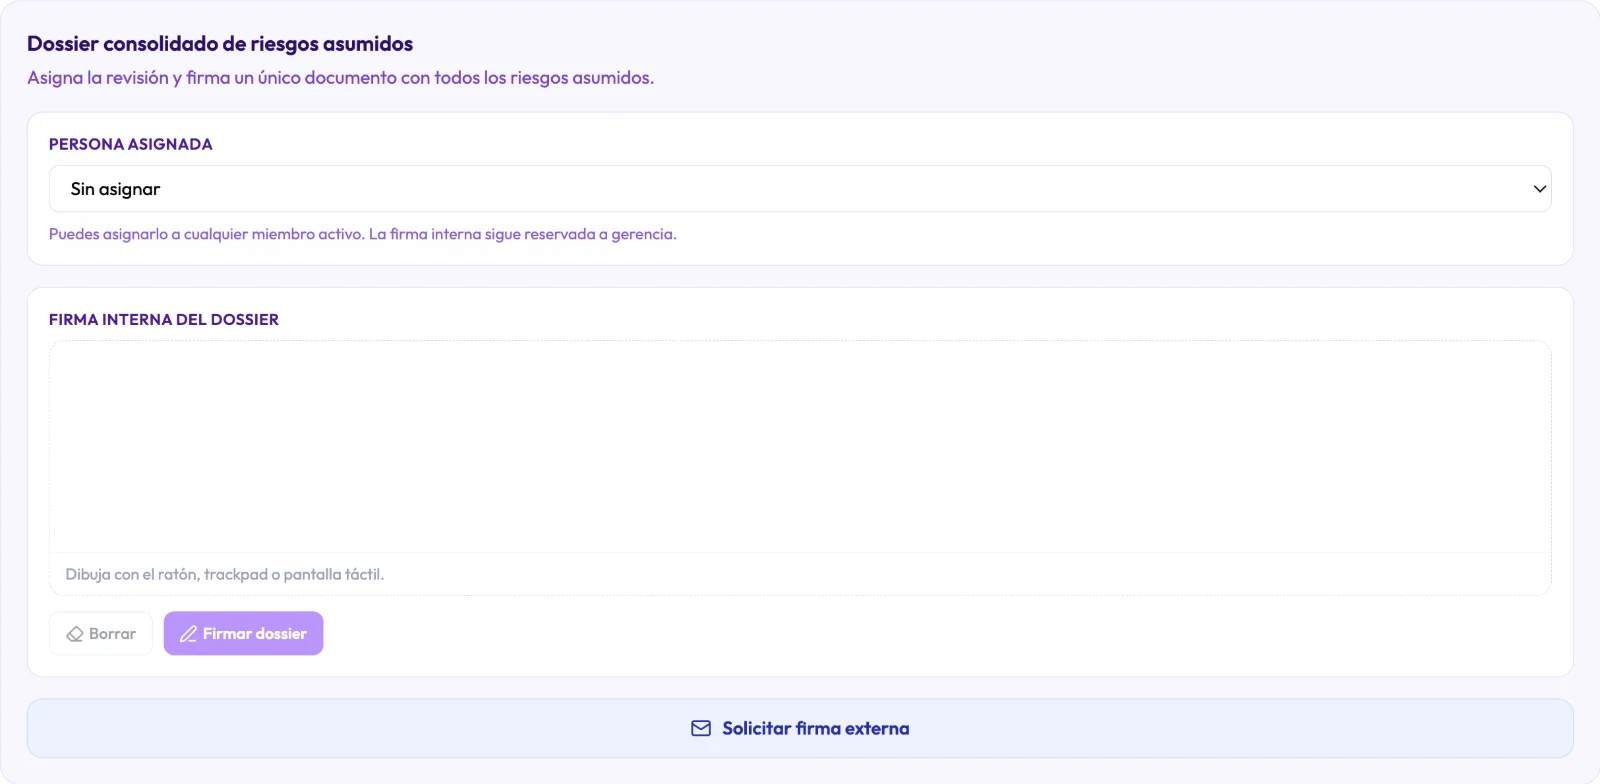
A consolidated PDF with all accepted risks for approval.
Maturity radar by framework and a compliance heat map by section.
Some features depend on your plan and active modules.
Management approval
When the organization decides to accept or transfer a risk, Audexa keeps the justification, the owner and the residual risk, and gathers them in a dossier that management reviews and signs in one go. Signatures can be internal or requested by email.
How it works
Gaps from any framework become risks with a scenario and a rating.
Adjust the rating on the matrix and choose to mitigate, accept or transfer.
Collect management's signature, carry out the tasks and review the residual risk.
Frequently asked questions
No. Audexa generates a risk for each gap with a suggested scenario and rating. Your team reviews and adjusts them and decides how to treat them.
Yes, if the decision is justified. Accepting or transferring a risk requires a justification, owner, date, residual rating and the signature of an owner or administrator.
Not necessarily. The evidence has to be reviewed and the residual risk assessed.
The risk matrix and the accepted-risk dossier are available from the Core plan. Mitigation tasks are available from Premium.
Request a demo
In 30 minutes we turn an audit's gaps into risks, decide their treatment and generate the dossier for management.