
Governance
Approved and signed policies, defined roles and management oversight based on up-to-date data.
Governance · Risk · Compliance
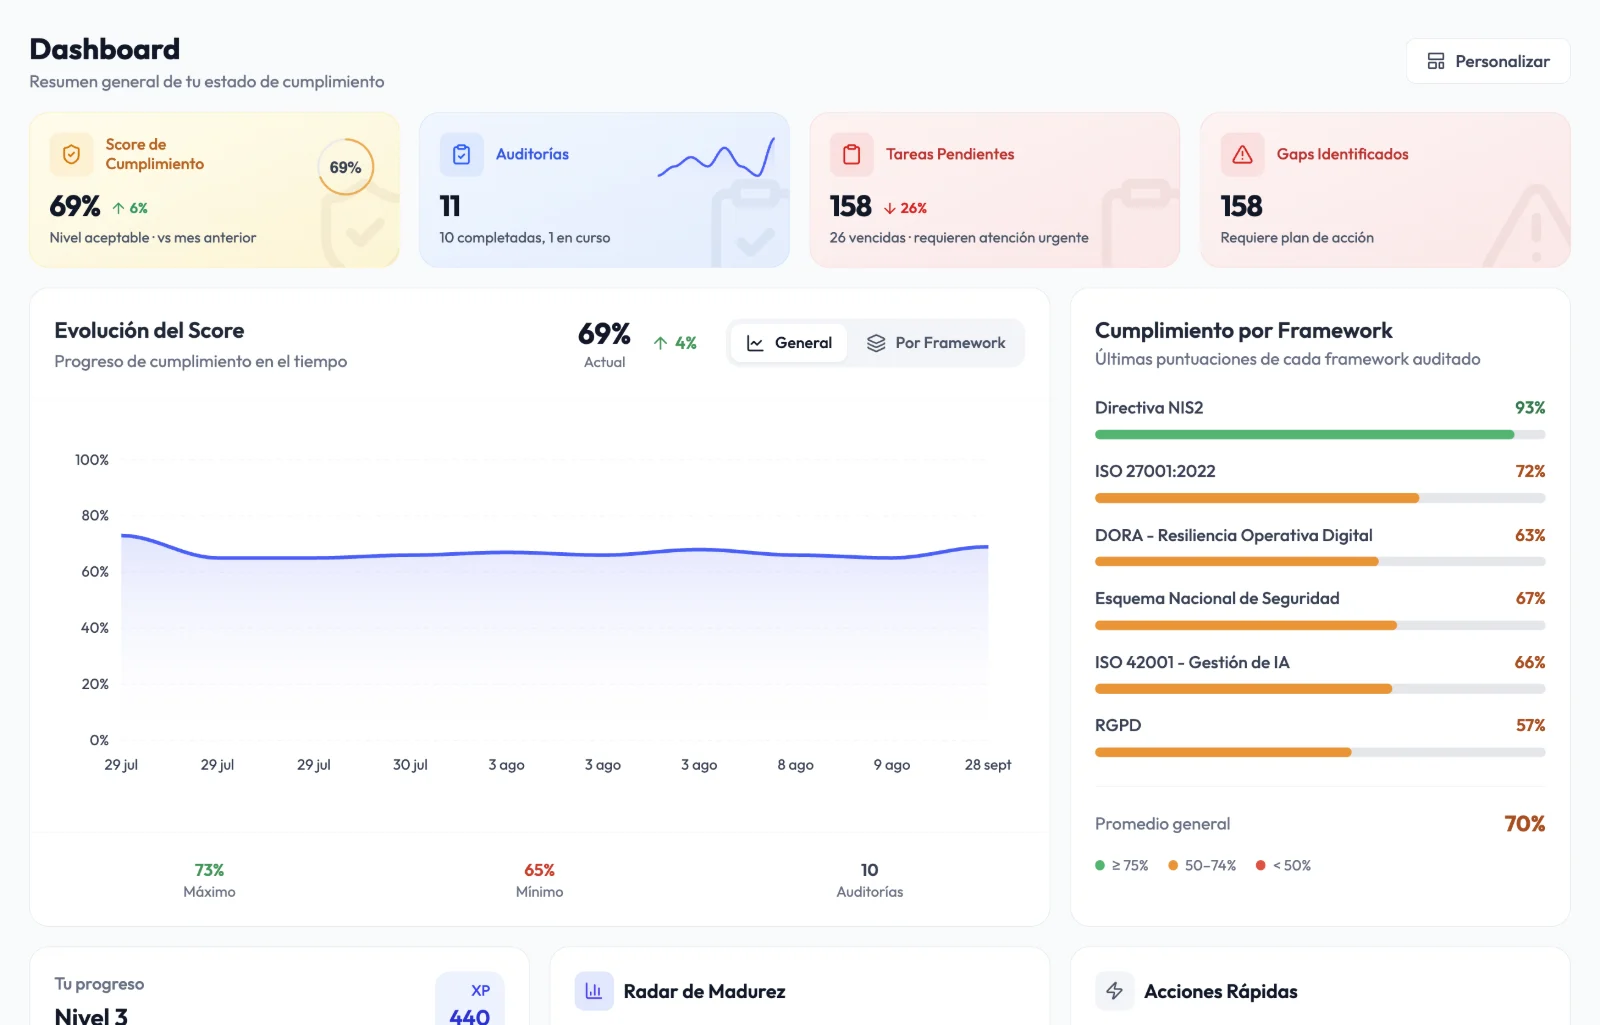
Audexa brings together audits across 13 frameworks, risk management, policies, evidence, assets and management reporting in one platform. Do the work once and use it for several standards.
Why a GRC platform
Every new regulation (NIS2, DORA, the AI Act) adds requirements that overlap with the previous ones. Without a platform, the same work is repeated in every audit and management has no single view.
Approved and signed policies, defined roles and management oversight based on up-to-date data.
Risks derived from real gaps, rated by likelihood and impact, with traceable treatment and acceptance.
Audits per framework, reusable evidence and an action plan you can track and prove.
What's included
Every module shares data with the others: a piece of evidence, a risk or a task is visible from every framework it affects.
Audit and measure against each standard.
NIS2, DORA, ISO 27001, ISO 27018, ENS, GDPR, NIST CSF 2.0, ISO 22301, ISO 42001, ISO 9001, ISO 14001, TPRM and whistleblowing channel.
Scheduled re-audits, cycle-to-cycle comparison and Statement of Applicability.
Registration, classification and obligations under the EU AI Act.
Prioritize what really matters.
Risks derived from gaps, with treatment and acceptance signed by management.
Devices, software, SaaS, suppliers and contracts with an owner and periodic review.
vRadar matches your inventory against known vulnerabilities and creates remediation tasks.
Decide, document and report.
52 templates with versions, approval and internal or link-based signing.
A private evidence vault with expiry, review and history.
Executive and technical reports in PDF, Excel and Word, plus a configurable dashboard.
Some features depend on your plan and active modules.
Multi-framework
Cross-framework mappings let you reuse evidence and suggest reviewable answers when coverage is high. A control is never marked as compliant automatically.
Integrations
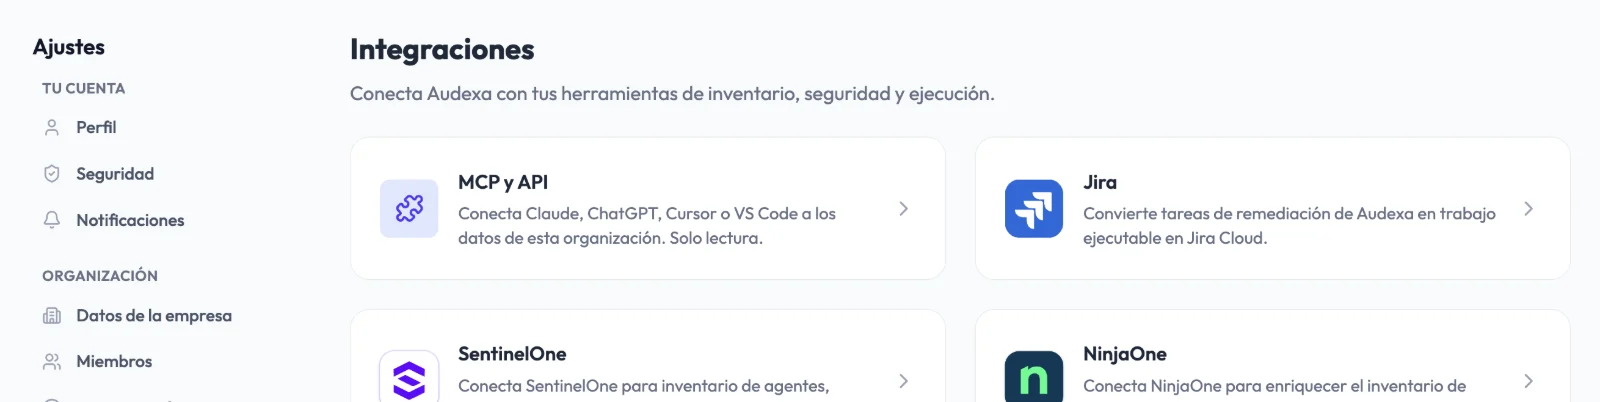
Your inventory is fed by your device management and security tools, tasks can become Jira issues, and the read-only REST API and MCP server let you query your compliance from other systems.
How it works
Start with the most urgent standard and add the rest, reusing the work already done.
Guided audits, weighted gaps and risks rated by likelihood and impact.
Tasks with owners, signed policies, current evidence and reports for management.
Before and after
Overall view
One Excel file per standard
Dashboard covering every framework
Risks
Matrix isolated from compliance
Risks derived from real gaps
Evidence
Duplicated in every audit
One piece of evidence for several controls
Policies
Word files with no version or signature
Lifecycle with approval and signature
Reporting
Manual slide decks
Exportable executive reports
Frequently asked questions
A platform that brings together governance (policies, roles, decisions), risk management and regulatory compliance so the organization manages them in a connected way rather than in isolated documents.
NIS2, DORA, ISO 27001, ISO 27018, ENS, GDPR, NIST CSF 2.0, ISO 22301, ISO 42001, ISO 9001, ISO 14001, third-party risk management (TPRM) and whistleblowing channel (Spain's Law 2/2023), plus the AI Governance module for the AI Act. Framework availability depends on the plan.
Not only. Audexa is designed so that a small IT, security or compliance team can run the program without relying on ongoing consulting, and it scales to organizations with several teams.
It's a web platform: you can start your first audit the same day. Assets, policies and evidence are loaded progressively.
Interface, frameworks, policies and reports in Spanish, English, French, Italian and German.
Audexa runs on EU infrastructure, with role-based access, two-factor authentication and activity traceability.
Request a demo
In 30 minutes we look at your starting point, the frameworks that apply to you and what your GRC program would look like in Audexa.