
Current version
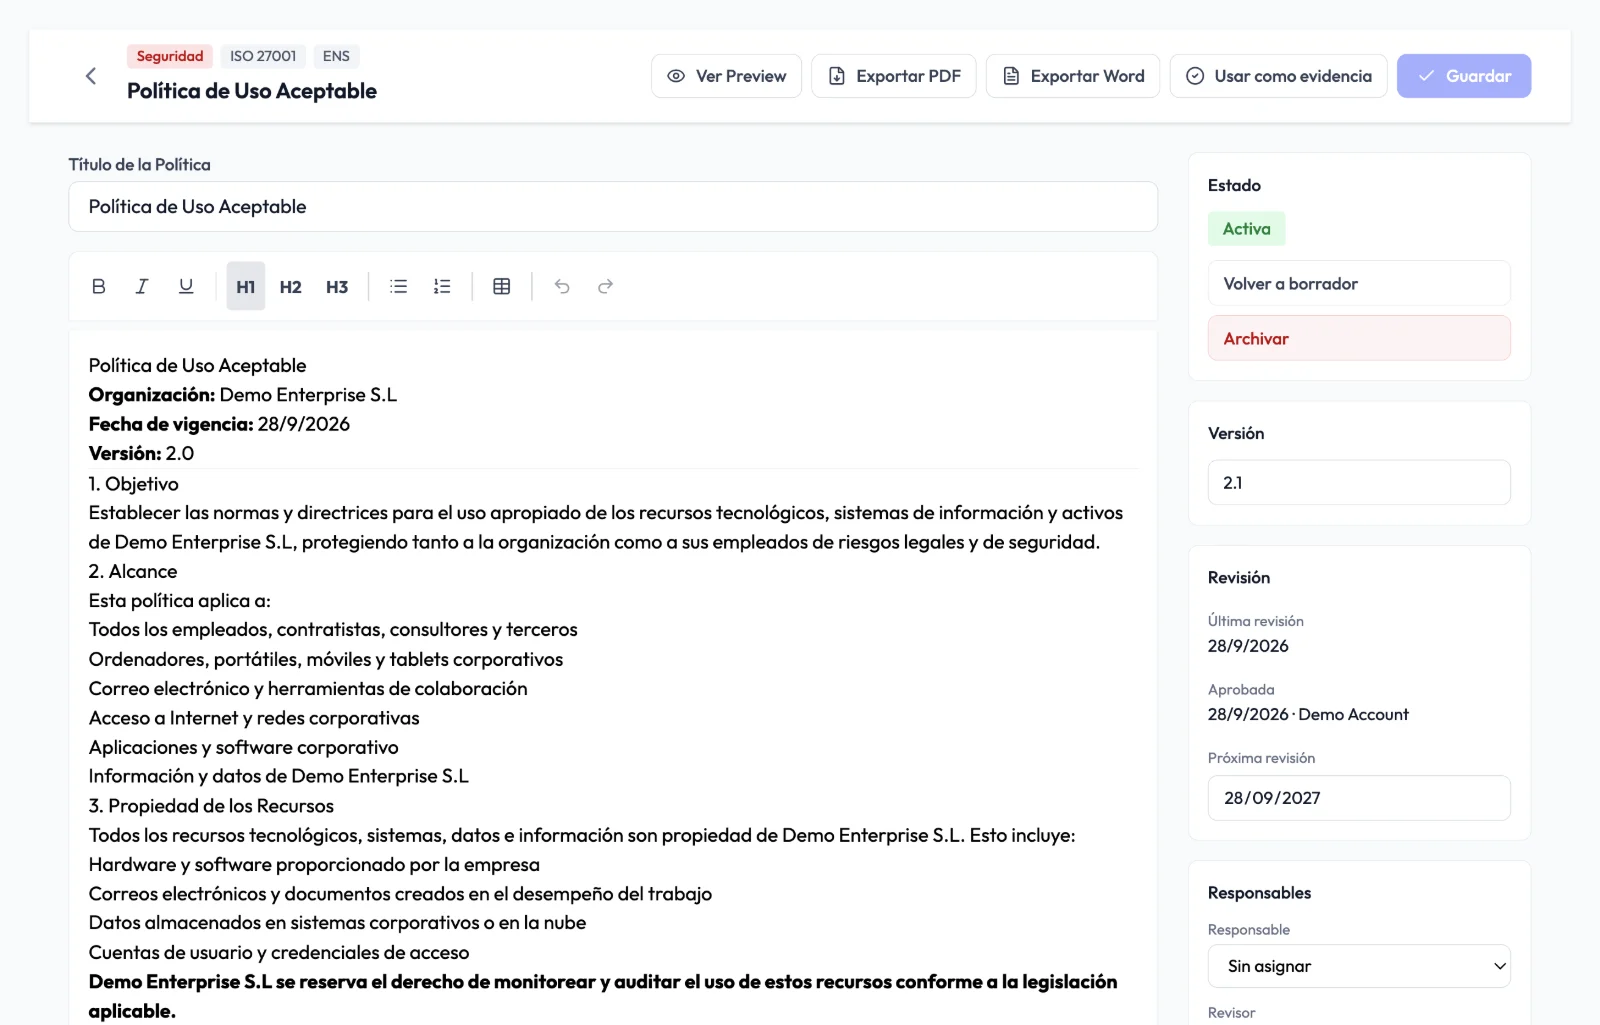
A single approved version, with change history and the option to restore.
Policy library
Start from 52 templates in five languages, tailor them with your company's details and manage their full lifecycle: review, approval, signature, versions and export to Word. Every approved policy can serve as evidence in your audits.
Why it matters
ISO 27001, NIS2, ENS, GDPR and DORA require documented policies. Writing them is rarely the problem: the hard part is keeping them up to date, knowing which version is current and proving who approved it and when.
A single approved version, with change history and the option to restore.
Who reviewed, who approved and who signed, with the date and a fingerprint of the exact version.
A next-review date and an owner, so no policy goes out of date unnoticed.
How Audexa helps
Drafting, governance and evidence in one place, connected to the frameworks you audit.
Start from a solid foundation.
Security, privacy, operations, compliance and HR, linked to each framework.
Company name, DPO, owners or review dates are filled in automatically across all policies.
Fonts, headers, colors, logo, classification levels and section numbering.
Control of the full lifecycle.
Draft, in review, active and archived, with versions and restore points.
Drawn signature or an email request with a single-use link valid for 14 days.
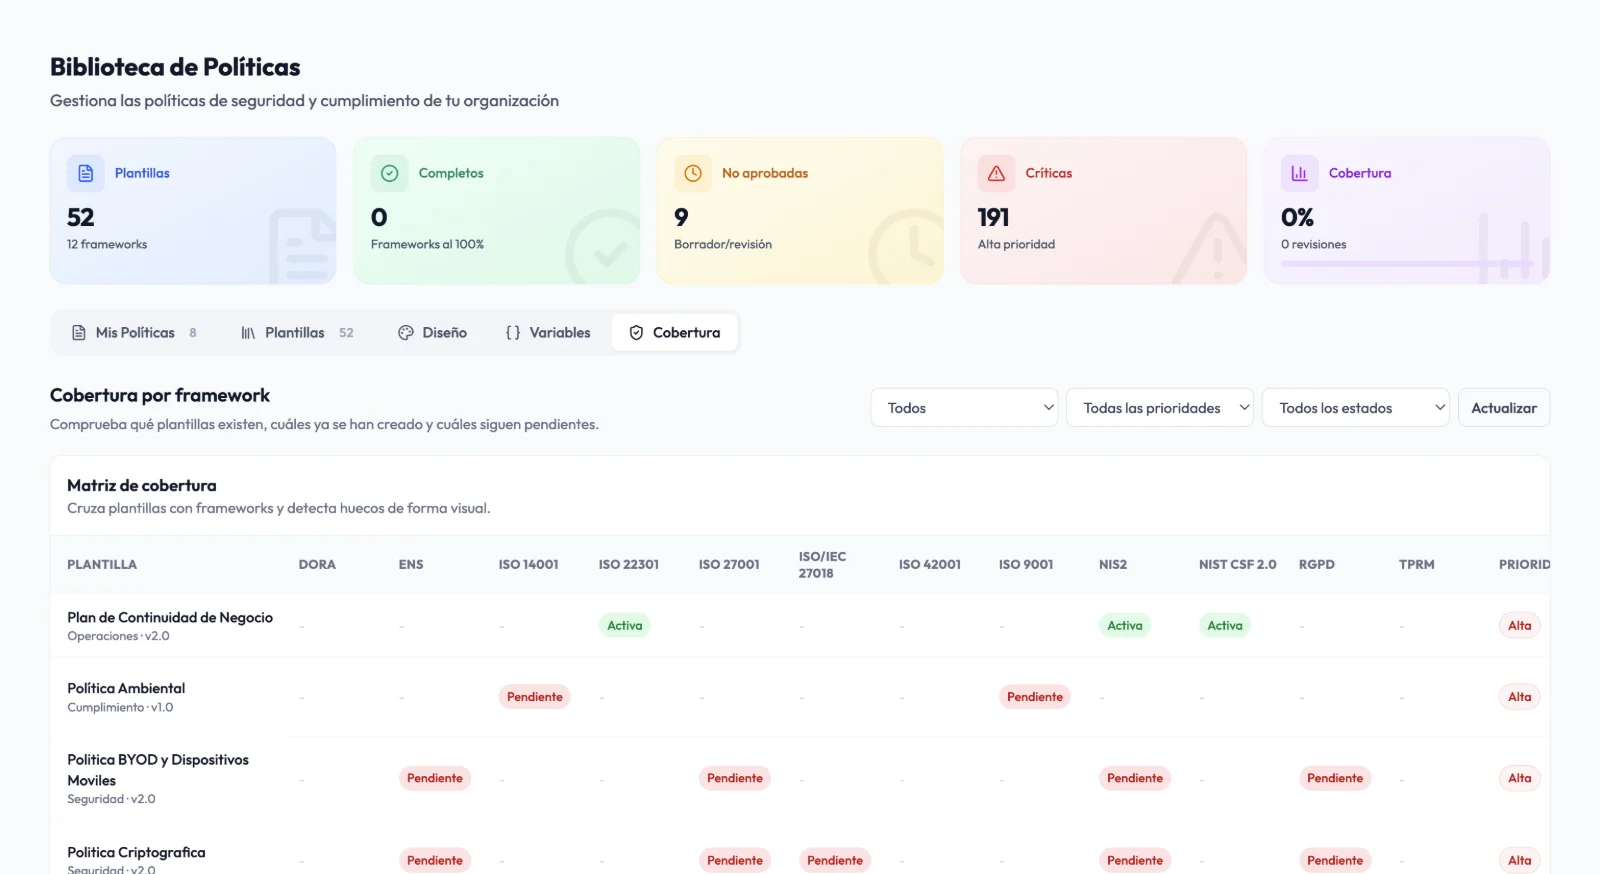
Which policies each standard requires, which you have and which are missing, by priority and status.
Policies as proof of compliance.
Save an immutable copy of the active version in the evidence vault.
Download in Word or PDF with your organization's design.
SHA-256 fingerprint of the signed version: if the policy changes, a new signature is required.
Some features depend on your plan and active modules.
Templates
The templates cover the areas that come up most often in audits and are linked to the frameworks you manage: 43 to ISO 27001, 39 to ENS, 35 to NIS2, 20 to GDPR and 4 specific to DORA.
Signing
Send a signature request to a team member or any email address. The link is single-use, expires in 14 days and is tied to the exact version of the document.
How it works
Filter by framework and priority and start with the policies you're missing.
Fill in the variables, adjust the text and send it for review and approval.
Collect signatures, export to Word and save it as evidence for the control.
Before and after
Starting point
A blank page or generic templates
52 templates linked to each standard
Current version
“policy_final_v3_FINAL.docx”
One approved version with history
Signatures
Emails and scanned PDFs
Link-based signing with a version fingerprint
Review
Forgotten until the audit
Review date and owner
Evidence
Attaching the Word file by hand
Immutable copy in the evidence vault
Frequently asked questions
They're a solid starting point, but every policy must be adapted to your organization's reality. Variables and the editor make that quick, and the review workflow ensures someone validates the policy before it's approved.
Word (.docx) and PDF, with your organization's design and branding.
It's an internal approval signature with traceability (who, when and which version), designed to demonstrate policy governance to auditors. It does not replace a qualified electronic signature.
All 52 templates are available in Spanish, English, French, Italian and German.
The policy library is included in the Premium and Diamond plans and can also be purchased as a separate module.
Request a demo
In 30 minutes we create a policy from a template, take it through review and signature and turn it into evidence.